


According to security experts at Check Point the creators of the Nuclear EK are gaining nearly 100K USD each month with most victims in Europe and US
Most people want to work with a cloud business model nowadays, even malware programmers. More efficent than just one-time selling a security exploit, it has authors of malware now selling malware as a cloud-based service. This means they make money each time someone pays to rent one of them. Exploit kits (EKs) have been very effective in infecting end users. There are many EKs in the Malware-as-a-Service market, and Nuclear EK has been one of them since 2010.
“Developers create tools that they sell or rent to customers through online black markets, complete with sales, money-back guarantees and reputation systems to provide customers with assurances that they won’t get ripped off,” reads the 2016 Trustwave Global Security Report.
Like its competitors, the Nuclear EK is also rented to attackers for a limited time by creators and is ready to use via its control panel. According to the Check Point’s report, this panel is running on a nginx/1.8.0 server under a non-trivial port in order to hide itself from web crawlers. All of the control panels are fed by a master server. This master server contains Flash, JavaScript and VBScript exploits and pushes the malware onto targeted systems.
Check Point reports that they have found 15 active control panels for Nuclear which are rented for a few thousand dollars per month. It is estimated that the creators of the Nuclear EK are gaining nearly 100K USD each month.
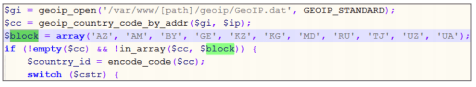
Authors of the code check the country from which the victim is browsing; it is not eligible for countries including Azerbaijan, Armenia, Belarus, Georgia, Kazakhstan, Kyrgyzstan, Moldova, Russia, Tajikistan, Uzbekistan and Ukraine, likely to avoid problems with the law in these countries.
Despite not running in these countries, Check Point statistics say that 1,846,678 machines were attacked and 184,568 machines were successfully exploited, nearly 10% success. As you can see in the graph below presenting successful infection rate per browser, the browser which has the highest percentage of success is Internet Explorer Version 8.

According to the report, Europe and US are the main targets. Despite many banking trojans that are distributed by the exploit kit, the number of ransomware infections is nearly three times that of banking trojan infections.

Studies made by Bitdefender shows us that:
- Half of users can’t accurately identify ransomware
- Half of victims are willing to pay up to $500 to recover encrypted data. This means according to the graph below, there are nearly 200K infected users . If half of them pay 500 USD, it makes a total of 50,000,000 USD !
- Personal documents rank first among user priorities.
- UK consumers would pay most to retrieve files.
- US users are the main target for ransomware.
 Written by: Süleyman Petek
Süleyman Petek is an application security guy and also he loves to write code.
He has been on enterprise level projects since 2005 as a developer, as a scrum master and also as a software architect.
Living in Istanbul-Turkey and trying to keep alive his weblogs at www.suleymanpetek.com
(Security Affairs – Nuclear EK, malware)
The post Creators of the Nuclear EK are gaining nearly 100K USD each month appeared first on Security Affairs.


